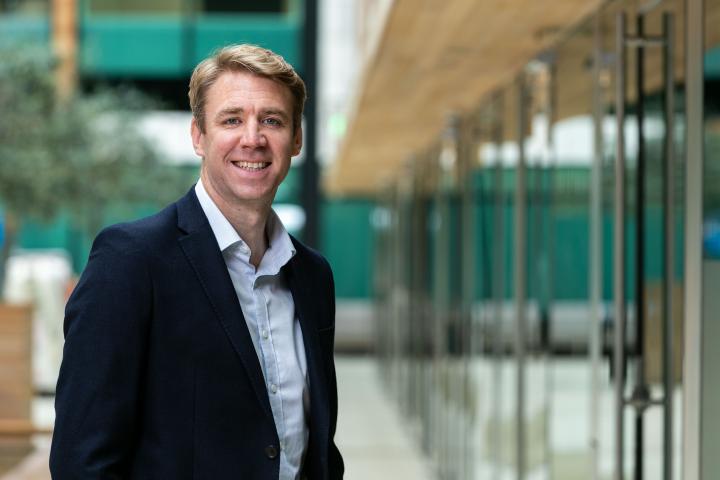
Richard Ford, CTO, Integrity360, comments:
“These vulnerabilities affect PHP installations serving web requests, putting a significant number of websites and applications at risk. Apache installations using mod php are particularly exposed, with a working proof-of-concept exploit already demonstrated.
“One of the underlying bugs reportedly dates back to 2004 and was only identified through AI-assisted analysis, showing how new technology can uncover weaknesses that have remained hidden for decades.
“Patching is the only complete fix. Organisations need to update affected systems urgently and should consider taking internet-facing services offline if they cannot patch immediately. They should also assess whether systems have already been compromised, looking for indicators such as unexpected shell activity or suspicious outbound web requests.
“As we saw with Log4Shell, a major challenge will be identifying where vulnerable software is embedded in third-party applications. Businesses need to work closely with their suppliers to establish their exposure and confirm what action is being taken. The risk extends beyond systems they manage directly.”
Read the Autumn 2026 edition free online →
Stay connected with NI's tech community: